E-signature for financial services
Banks, insurers and finance companies can use SahlSign today for the documents their compliance team clears for electronic signature — with evidence auditors can follow.
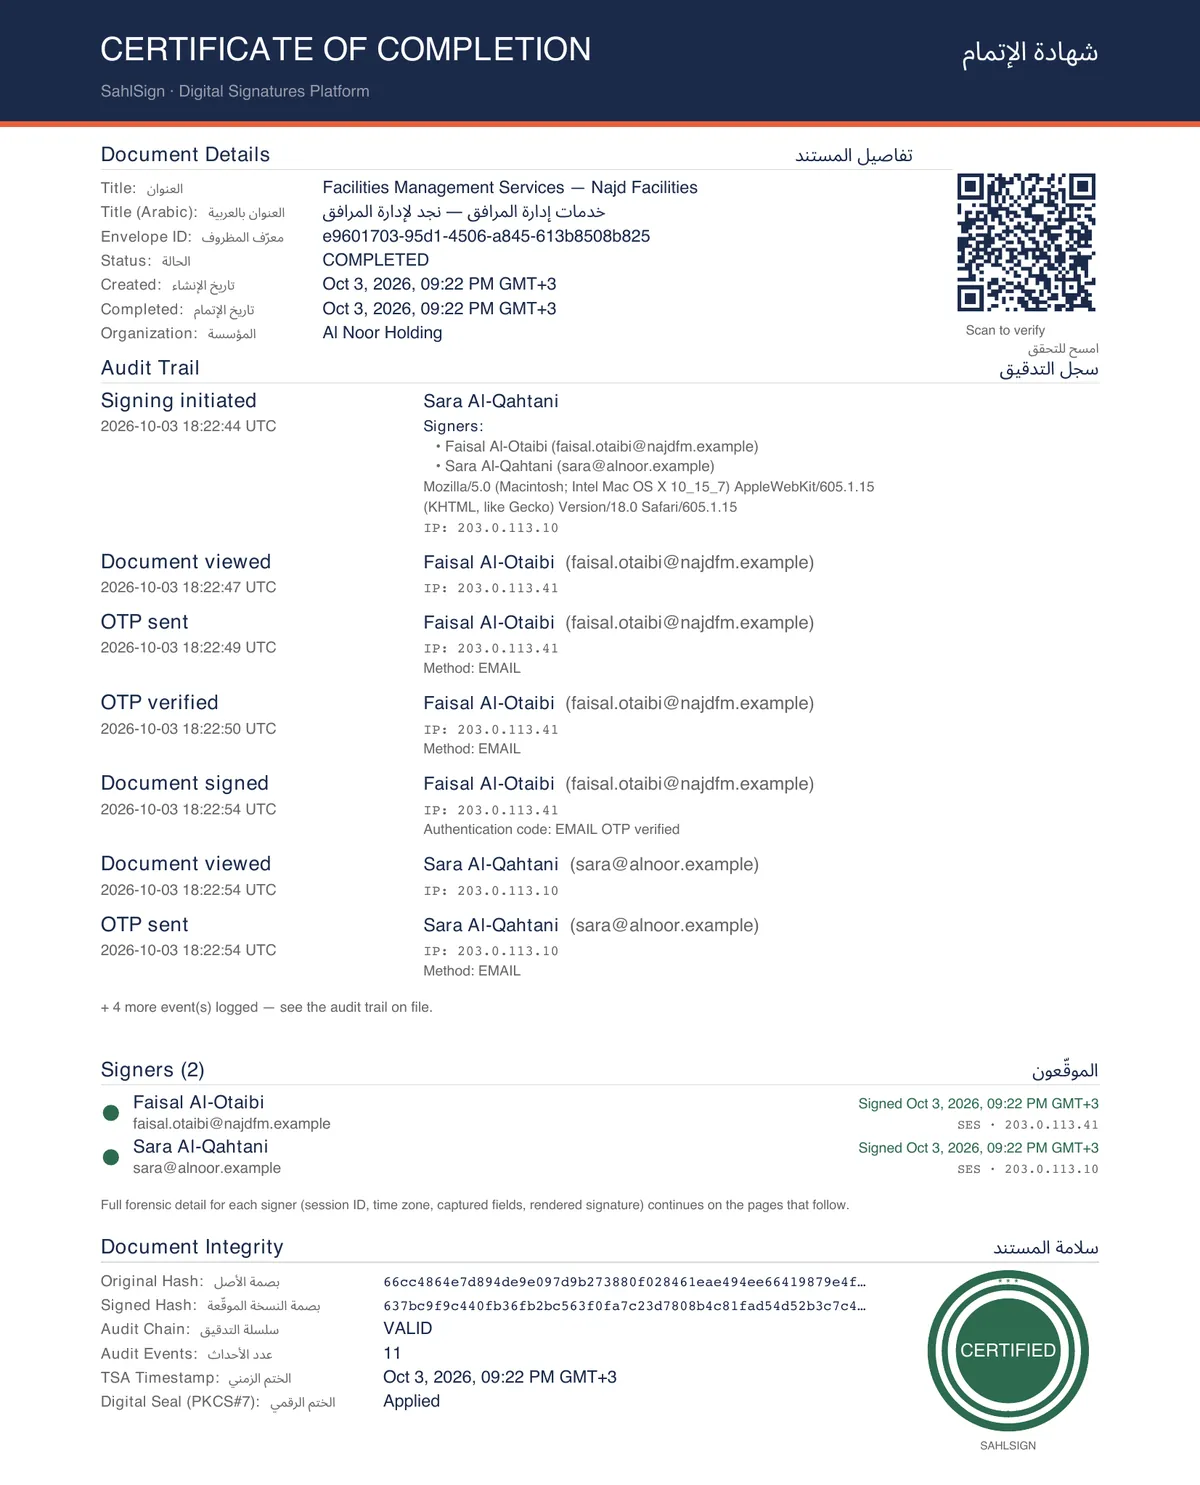
- Hash-chained audit trail
- SHA-256Hash-chained audit trail
- One-time code before every signature
- OTPOne-time code before every signature
- Signing page, emails and certificate
- AR + ENSigning page, emails and certificate
- Independent timestamp on every seal
- RFC 3161Independent timestamp on every seal
Banking, insurance and finance documents
Banking
Internal approvals, vendor and partner agreements, and employee documents — routed by value and signed in order.
Insurance
Broker and agency agreements and customer acknowledgements that your compliance team allows to be signed electronically.
KYC documents
Customer declarations and consent forms signed after an email one-time code. SahlSign does not perform identity verification against national ID.
Customer agreements
Bilingual agreements with a sealed PDF and a certificate the customer can verify by scanning its QR code.
Evidence an auditor can follow
A complete record
Consent, one-time code, signature and every hand-over in a hash-chained trail that is checked every night.
Separation of duties
The person who submits a contract can never approve it, and approvals are tied to the exact version.
What SahlSign does not offer yet
- Signing with a certificate from a DGA-licensed provider (often with Nafath identity verification) — required for many regulated customer instruments.
- Hosting inside Saudi Arabia: documents and the application are hosted outside the GCC.
- ISO 27001 or SOC 2 certification, and the documentation SAMA cloud-outsourcing reviews usually ask for.
Everything else on this page is live today.
Frequently asked questions
Can we use SahlSign for customer onboarding?
Only for documents your compliance team accepts with email one-time-code verification. Where regulation requires certificate-based signing, Nafath identity verification or in-Kingdom data, SahlSign is not suitable yet — talk to us about your case.
Where is data stored?
Encrypted, outside the GCC, in the same region as the application. There is no GCC hosting option yet.
Check fit with our team
Tell us which documents you want to sign and we will say plainly whether SahlSign fits today.
Talk to sales